

Önceki sürümlerde olduğu gibi Android 16'da da uygulamanızı etkileyebilecek davranış değişiklikleri vardır. Aşağıdaki davranış değişiklikleri yalnızca Android 16 veya sonraki sürümleri hedefleyen uygulamalar için geçerlidir. Uygulamanız Android 16 veya sonraki sürümleri hedefliyorsa geçerli olduğu durumlarda bu davranışları destekleyecek şekilde uygulamanızı değiştirmeniz gerekir.
Uygulamanızın targetSdkVersion değerinden bağımsız olarak Android 16'da çalışan tüm uygulamaları etkileyen davranış değişiklikleri listesini de inceleyin.
Kullanıcı deneyimi ve sistem arayüzü
Android 16 (API düzeyi 36), daha tutarlı ve sezgisel bir kullanıcı deneyimi sunmak için aşağıdaki değişiklikleri içerir.
Uçtan uca kapsamı dışında kalmayı seçme seçeneği kaldırılıyor
Android 15 强制要求以 Android 15(API 级别 35)为目标平台的应用采用边到边模式,但您的应用可以通过将 R.attr#windowOptOutEdgeToEdgeEnforcement 设置为 true 来选择退出此模式。对于以 Android 16(API 级别 36)为目标平台的应用,R.attr#windowOptOutEdgeToEdgeEnforcement 已废弃并停用,并且您的应用无法选择停用边到边模式。
- 如果您的应用以 Android 16(API 级别 36)为目标平台,并且在 Android 15 设备上运行,
R.attr#windowOptOutEdgeToEdgeEnforcement会继续运行。 - 如果您的应用以 Android 16(API 级别 36)为目标平台,并且在 Android 16 设备上运行,则
R.attr#windowOptOutEdgeToEdgeEnforcement会处于停用状态。
如需在 Android 16 中进行测试,请确保您的应用支持无边框,并移除对 R.attr#windowOptOutEdgeToEdgeEnforcement 的任何使用,以便您的应用在 Android 15 设备上也支持无边框。如需支持边到边,请参阅 Compose 和视图指南。
Tahmin edilen geri gitme için taşıma veya kapsam dışında kalmayı seçme gerekiyor
对于以 Android 16(API 级别 36)或更高版本为目标平台且在搭载 Android 16 或更高版本的设备上运行的应用,系统会默认启用预测性返回系统动画(返回主屏幕、跨任务和跨 activity)。此外,系统不会调用 onBackPressed,也不会再分派 KeyEvent.KEYCODE_BACK。
如果您的应用会拦截返回事件,而您尚未迁移到预测性返回,请更新应用以使用受支持的返回导航 API,或在应用的 AndroidManifest.xml 文件的 <application> 或 <activity> 标记中将 android:enableOnBackInvokedCallback 属性设置为 false,以暂时停用预测性返回。
Zarif yazı tipi API'lerinin desteği sonlandırıldı ve devre dışı bırakıldı
以 Android 15(API 级别 35)为目标平台的应用默认将 elegantTextHeight
TextView 属性设置为 true,从而将紧凑型字体替换为可读性更高的字体。您可以通过将 elegantTextHeight 属性设置为 false 来替换此设置。
Android 16 弃用了 elegantTextHeight 属性,当您的应用以 Android 16 为目标平台后,系统会忽略该属性。由这些 API 控制的“界面字体”即将停用,因此您应调整所有布局,以确保阿拉伯语、老挝语、缅甸语、泰米尔语、古吉拉特语、卡纳达语、马拉雅拉姆语、奥里亚语、泰卢固语或泰语文本的呈现效果一致且不受未来变化的影响。
elegantTextHeight 属性设置为 false 替换默认值的应用,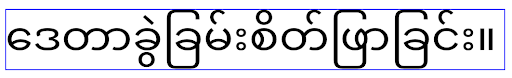
elegantTextHeight 行为。elegantTextHeight 属性设置为 false 来替换默认值的应用,其 elegantTextHeight 行为。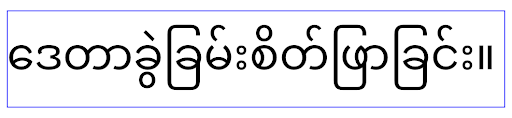
Temel işlevler
Android 16 (API düzeyi 36), Android sisteminin çeşitli temel özelliklerini değiştiren veya genişleten aşağıdaki değişiklikleri içerir.
Sabit ücretli çalışma planlaması optimizasyonu
在以 Android 16 为目标平台之前,如果 scheduleAtFixedRate 因不在有效的进程生命周期内而错过了任务执行,则当应用返回到有效的生命周期时,所有错过的执行会立即执行。
以 Android 16 为目标平台时,当应用返回到有效的生命周期时,系统会立即执行最多 1 次未执行的 scheduleAtFixedRate 执行。此行为变更预计会提升应用性能。在您的应用中测试此行为,检查您的应用是否受到影响。您还可以使用应用兼容性框架并启用 STPE_SKIP_MULTIPLE_MISSED_PERIODIC_TASKS 兼容性标志进行测试。
Cihaz form faktörleri
Android 16 (API düzeyi 36), büyük ekranlı cihazlarda görüntülenen uygulamalar için aşağıdaki değişiklikleri içerir.
Uyarlanabilir düzenler
With Android apps now running on a variety of devices (such as phones, tablets, foldables, desktops, cars, and TVs) and windowing modes on large screens (such as split screen and desktop windowing), developers should build Android apps that adapt to any screen and window size, regardless of device orientation. Paradigms like restricting orientation and resizability are too restrictive in today's multidevice world.
Ignore orientation, resizability, and aspect ratio restrictions
For apps targeting Android 16 (API level 36), orientation, resizability, and aspect ratio restrictions no longer apply on displays with smallest width >= 600dp. Apps fill the entire display window, regardless of aspect ratio or a user's preferred orientation, and pillarboxing isn't used.
This change introduces a new standard platform behavior. Android is moving toward a model where apps are expected to adapt to various orientations, display sizes, and aspect ratios. Restrictions like fixed orientation or limited resizability hinder app adaptability. Make your app adaptive to deliver the best possible user experience.
You can also test this behavior by using the
app compatibility framework and enabling the
UNIVERSAL_RESIZABLE_BY_DEFAULT compat flag.
Common breaking changes
Ignoring orientation, resizability, and aspect ratio restrictions might impact your app's UI on some devices, especially elements that were designed for small layouts locked in portrait orientation: for example, issues like stretched layouts and off-screen animations and components. Any assumptions about aspect ratio or orientation can cause visual issues with your app. Learn more about how to avoid them and improve your app's adaptive behaviour.
Allowing device rotation results in more activity re-creation, which can result in losing user state if not properly preserved. Learn how to correctly save UI state in Save UI states.
Implementation details
The following manifest attributes and runtime APIs are ignored across large screen devices in full-screen and multi-window modes:
screenOrientationresizableActivityminAspectRatiomaxAspectRatiosetRequestedOrientation()getRequestedOrientation()
The following values for screenOrientation, setRequestedOrientation(), and
getRequestedOrientation() are ignored:
portraitreversePortraitsensorPortraituserPortraitlandscapereverseLandscapesensorLandscapeuserLandscape
Regarding display resizability, android:resizeableActivity="false",
android:minAspectRatio, and android:maxAspectRatio have no effect.
For apps targeting Android 16 (API level 36), app orientation, resizability, and aspect ratio constraints are ignored on large screens by default. Every app that isn't fully ready can temporarily override this behavior by opting out, which results in the previous behavior of being placed in compatibility mode.
Exceptions
The Android 16 orientation, resizability, and aspect ratio restrictions don't apply in the following situations:
- Games (based on the
android:appCategoryflag) - Users explicitly opting in to the app's default behavior in aspect ratio settings of the device
- Screens that are smaller than
sw600dp
Opt out temporarily
To opt out a specific activity, declare the
PROPERTY_COMPAT_ALLOW_RESTRICTED_RESIZABILITY manifest property:
<activity ...>
  <property android:name="android.window.PROPERTY_COMPAT_ALLOW_RESTRICTED_RESIZABILITY" android:value="true" />
  ...
</activity>
If too many parts of your app aren't ready for Android 16, you can opt out completely by applying the same property at the application level:
<application ...>
  <property android:name="android.window.PROPERTY_COMPAT_ALLOW_RESTRICTED_RESIZABILITY" android:value="true" />
</application>
Sağlık ve fitness
Android 16 (API düzeyi 36), sağlık ve fitness verileriyle ilgili aşağıdaki değişiklikleri içerir.
Sağlık ve fitness izinleri
For apps targeting Android 16 (API level 36) or higher,
BODY_SENSORS permissions use more granular permissions
under android.permissions.health, which Health Connect
also uses. As of Android 16, any API previously requiring BODY_SENSORS
or BODY_SENSORS_BACKGROUND requires the corresponding
android.permissions.health permission instead. This affects the following data
types, APIs, and foreground service types:
HEART_RATE_BPMfrom Health Services on Wear OSSensor.TYPE_HEART_RATEfrom Android Sensor ManagerheartRateAccuracyandheartRateBpmfromProtoLayouton Wear OSFOREGROUND_SERVICE_TYPE_HEALTHwhere the respectiveandroid.permission.healthpermission is needed in place ofBODY_SENSORS
If your app uses these APIs, it should request the respective granular permissions:
- For while-in-use monitoring of Heart Rate, SpO2, or Skin Temperature:
request the granular permission under
android.permissions.health, such asREAD_HEART_RATEinstead ofBODY_SENSORS. - For background sensor access: request
READ_HEALTH_DATA_IN_BACKGROUNDinstead ofBODY_SENSORS_BACKGROUND.
These permissions are the same as those that guard access to reading data from Health Connect, the Android datastore for health, fitness, and wellness data.
Mobile apps
Mobile apps migrating to use the READ_HEART_RATE and other granular
permissions must also declare an activity to display
the app's privacy policy. This is the same requirement as Health Connect.
Bağlantı
Android 16 (API düzeyi 36), çevre birimleriyle bağlantıyı iyileştirmek için Bluetooth yığınında aşağıdaki değişiklikleri içerir.
Bağlantı kaybını ve şifreleme değişikliklerini işlemek için yeni intent'ler
作为改进了对键值对丢失的处理的一部分,Android 16 还引入了 2 个新 intent,以便应用更好地了解键值对丢失和加密更改。
以 Android 16 为目标平台的应用现在可以:
- 在检测到远程键盘连接丢失时接收
ACTION_KEY_MISSINGintent,以便提供更具信息量的用户反馈并采取适当的措施。 - 每当链接的加密状态发生变化时,都会收到
ACTION_ENCRYPTION_CHANGEintent。这包括加密状态更改、加密算法更改和加密密钥大小更改。如果应用在稍后收到ACTION_ENCRYPTION_CHANGEintent 时成功加密了链接,则必须将该绑定视为已恢复。
适应不同的 OEM 实现
虽然 Android 16 引入了这些新 intent,但其实现和广播可能会因不同的设备制造商 (OEM) 而异。为了确保您的应用在所有设备上都能提供一致且可靠的体验,开发者应设计其绑定丢失处理机制,以妥善适应这些潜在的变化。
我们建议您采用以下应用行为:
如果广播
ACTION_KEY_MISSINGintent:系统会断开 ACL(异步无连接)链接,但会保留设备的配对信息(如此处所述)。
您的应用应将此 intent 用作检测配对丢失的主要信号,并在发起设备忘记或重新配对之前引导用户确认远程设备是否在范围内。
如果设备在收到
ACTION_KEY_MISSING后断开连接,您的应用应谨慎重新连接,因为设备可能已不再与系统绑定。如果未广播
ACTION_KEY_MISSINGintent:ACL 链接将保持连接状态,系统会移除设备的配对信息,与 Android 15 中的行为相同。
在这种情况下,您的应用应继续使用与之前的 Android 版本相同的现有配对丢失处理机制,以检测和管理配对丢失事件。
Bluetooth bağlantısını kaldırmanın yeni yolu
Android 16'yı hedefleyen tüm uygulamalar artık CompanionDeviceManager'teki herkese açık bir API'yi kullanarak Bluetooth cihazlarının eşlemesini kaldırabilir. Bir tamamlayıcı cihaz CDM ilişkisi olarak yönetiliyorsa uygulama, ilişkili cihazdaki yeni removeBond(int) API'yi kullanarak Bluetooth bağını kaldırmayı tetikleyebilir. Uygulama, Bluetooth cihaz yayın etkinliğini dinleyerek ACTION_BOND_STATE_CHANGED bağ durumu değişikliklerini izleyebilir.
Güvenlik
Android 16 (API düzeyi 36), aşağıdaki güvenlik değişikliklerini içerir.
MediaStore sürümünü kilitleme
对于以 Android 16 或更高版本为目标平台的应用,MediaStore#getVersion() 现在将是每个应用的唯一标识。这会从版本字符串中移除标识属性,以防止滥用和用于指纹识别技术。应用不应对此版本的格式做出任何假设。在使用此 API 时,应用应已处理版本变更,并且在大多数情况下无需更改其当前行为,除非开发者尝试推断超出此 API 预期范围的其他信息。
Daha Güvenli Intent'ler
更安全的 intent 功能是一项多阶段安全计划,旨在提高 Android intent 解析机制的安全性。其目标是在 intent 处理期间添加检查并过滤不符合特定条件的 intent,从而保护应用免受恶意操作的影响。
在 Android 15 中,该功能侧重于发送应用。现在,在 Android 16 中,控制权转移到了接收应用,开发者可以使用其应用清单选择启用严格 intent 解析。
我们将实施两项关键变更:
显式 intent 必须与目标组件的 intent 过滤器相匹配:如果 intent 显式定位到某个组件,则应与该组件的 intent 过滤器相匹配。
不含操作的 intent 无法匹配任何 intent 过滤器:未指定操作的 intent 不应解析为任何 intent 过滤器。
这些变更仅在涉及多个应用时适用,不会影响单个应用内的 intent 处理。
影响
由于该功能具有选择启用性质,因此开发者必须在其应用清单中明确启用该功能,它才能生效。 因此,该功能的影响范围仅限于满足以下条件的应用:
- 了解 Safer Intents 功能及其优势。
- 主动选择在应用中采用更严格的 intent 处理做法。
这种选择性启用的方法可最大限度地降低破坏现有应用的风险,这些应用可能依赖于当前安全性较低的 intent 解析行为。
虽然 Android 16 中的初始影响可能有限,但 Safer Intents 计划已制定路线图,将在未来的 Android 版本中产生更广泛的影响。 我们计划最终将严格 intent 解析设为默认行为。
Safer Intents 功能可以提高恶意应用利用 intent 解析机制中的漏洞的难度,从而显著增强 Android 生态系统的安全性。
不过,必须谨慎管理向停用和强制执行的过渡,以解决与现有应用的潜在兼容性问题。
实现
开发者需要在其应用清单中使用 intentMatchingFlags 属性明确启用更严格的 intent 匹配。以下示例展示了如何为整个应用选择启用该功能,但为某个接收器停用/选择退出该功能:
<application android:intentMatchingFlags="enforceIntentFilter">
    <receiver android:name=".MyBroadcastReceiver" android:exported="true" android:intentMatchingFlags="none">
        <intent-filter>
            <action android:name="com.example.MY_CUSTOM_ACTION" />
        </intent-filter>
        <intent-filter>
            <action android:name="com.example.MY_ANOTHER_CUSTOM_ACTION" />
        </intent-filter>
    </receiver>
</application>
详细了解支持的标志:
| 标志名称 | 说明 |
|---|---|
| enforceIntentFilter | 对传入 intent 强制执行更严格的匹配 |
| 无 | 停用传入 intent 的所有特殊匹配规则。指定多个标志时,如果值存在冲突,则优先采用“none”标志 |
| allowNullAction | 放宽匹配规则,允许不含操作的 intent 进行匹配。此标志将与“enforceIntentFilter”结合使用,以实现特定行为 |
测试和调试
强制执行生效后,如果 intent 调用方已正确填充 intent,应用应能正常运行。
不过,被屏蔽的 intent 会触发警告日志消息,例如带有 "PackageManager." 标记的 "Intent does not match component's intent filter:" 和 "Access blocked:"。这表示存在可能影响应用的潜在问题,需要引起注意。
Logcat 过滤条件:
tag=:PackageManager & (message:"Intent does not match component's intent filter:" | message: "Access blocked:")
GPU sistem çağrısı filtreleme
为了强化 Mali GPU 表面,已废弃或仅用于 GPU 开发的 Mali GPU IOCTL 已在正式版 build 中被屏蔽。此外,用于 GPU 性能分析的 IOCTL 已限制为 shell 进程或可调试应用。如需详细了解平台级政策,请参阅 SAC 更新。
此变更适用于使用 Mali GPU 的 Pixel 设备(Pixel 6-9)。Arm 在其 r54p2 版本的 Documentation/ioctl-categories.rst 中提供了其 IOCTL 的官方分类。此列表将在未来的驱动程序版本中继续维护。
此项变更不会影响受支持的图形 API(包括 Vulkan 和 OpenGL),预计也不会影响开发者或现有应用。 GPU 性能分析工具(例如 Streamline Performance Analyzer 和 Android GPU 检查器)不会受到影响。
测试
如果您看到类似以下内容的 SELinux 拒绝,则您的应用可能已受到此变更的影响:
06-30 10:47:18.617 20360 20360 W roidJUnitRunner: type=1400 audit(0.0:85): avc:  denied  { ioctl }
for  path="/dev/mali0" dev="tmpfs" ino=1188 ioctlcmd=0x8023
scontext=u:r:untrusted_app_25:s0:c512,c768 tcontext=u:object_r:gpu_device:s0 tclass=chr_file
permissive=0 app=com.google.android.selinux.pts
如果您的应用需要使用被屏蔽的 IOCTL,请提交 bug 并将其分配给 android-partner-security@google.com。
常见问题解答
此政策变更是否适用于所有 OEM? 此项变更将采用选择启用的方式,但任何想要使用此加固方法的 OEM 都可以使用。如需了解如何实现此变更,请参阅实现文档。
是否必须在 OEM 代码库中进行更改才能实现此功能,还是说新的 AOSP 版本默认提供此功能? 默认情况下,平台级变更将随新的 AOSP 版本一起发布。如果供应商希望应用此更改,可以在其代码库中选择启用此更改。
SoC 是否负责确保 IOCTL 列表保持最新状态?例如,如果我的设备使用 ARM Mali GPU,我是否需要就任何更改与 ARM 联系? 各个 SoC 必须在驱动程序发布时更新其每个设备的 IOCTL 列表。 例如,ARM 会在驱动程序更新时更新其发布的 IOCTL 列表。 不过,OEM 应确保将这些更新纳入其 SEPolicy 中,并根据需要将任何选定的自定义 IOCTL 添加到列表中。
此变更会自动应用于所有在售 Pixel 设备,还是需要用户执行操作来切换某些设置才能应用此变更? 此变更适用于所有使用 Mali GPU 的 Pixel 在售设备(Pixel 6-9)。用户无需采取任何行动即可应用此变更。
使用此政策是否会影响内核驱动程序的性能? 此政策已在 Mali GPU 上使用 GFXBench 进行了测试,未观察到 GPU 性能发生可测量的变化。
IOCTL 列表是否必须与当前用户空间和内核驱动程序版本保持一致? 是的,允许的 IOCTL 列表必须与用户空间和内核驱动程序支持的 IOCTL 同步。如果用户空间或内核驱动程序中的 IOCTL 发生更新,则 SEPolicy IOCTL 列表也必须进行更新以保持一致。
ARM 已将 IOCTL 分类为“受限”/“插桩”,但我们希望在生产用例中使用其中一些 IOCTL,和/或拒绝其他 IOCTL。 各个 OEM/SoC 负责根据其用户空间 Mali 库的配置,决定如何对所使用的 IOCTL 进行分类。 ARM 的列表可用于帮助确定这些设置,但每个 OEM/SoC 的用例可能有所不同。
Gizlilik
Android 16 (API düzeyi 36), aşağıdaki gizlilik değişikliklerini içerir.
Yerel Ağ İzni
Devices on the LAN can be accessed by any app that has the INTERNET permission.
This makes it easy for apps to connect to local devices but it also has privacy
implications such as forming a fingerprint of the user, and being a proxy for
location.
The Local Network Protections project aims to protect the user's privacy by gating access to the local network behind a new runtime permission.
Release plan
This change will be deployed between two releases, 25Q2 and 26Q2 respectively. It is imperative that developers follow this guidance for 25Q2 and share feedback because these protections will be enforced at a later Android release. Moreover, they will need to update scenarios which depend on implicit local network access by using the following guidance and prepare for user rejection and revocation of the new permission.
Impact
At the current stage, LNP is an opt-in feature which means only the apps that opt in will be affected. The goal of the opt-in phase is for app developers to understand which parts of their app depend on implicit local network access such that they can prepare to permission guard them for the next release.
Apps will be affected if they access the user's local network using:
- Direct or library use of raw sockets on local network addresses (e.g. mDNS or SSDP service discovery protocol)
- Use of framework level classes that access the local network (e.g. NsdManager)
Traffic to and from a local network address requires local network access permission. The following table lists some common cases:
| App Low Level Network Operation | Local Network Permission Required |
|---|---|
| Making an outgoing TCP connection | yes |
| Accepting incoming TCP connections | yes |
| Sending a UDP unicast, multicast, broadcast | yes |
| Receiving an incoming UDP unicast, multicast, broadcast | yes |
These restrictions are implemented deep in the networking stack, and thus they apply to all networking APIs. This includes sockets created in native or managed code, networking libraries like Cronet and OkHttp, and any APIs implemented on top of those. Trying to resolve services on the local network (i.e. those with a .local suffix) will require local network permission.
Exceptions to the rules above:
- If a device's DNS server is on a local network, traffic to or from it (at port 53) doesn't require local network access permission.
- Applications using Output Switcher as their in-app picker won't need local network permissions (more guidance to come in 2025Q4).
Developer Guidance (Opt-in)
To opt into local network restrictions, do the following:
- Flash the device to a build with 25Q2 Beta 3 or later.
- Install the app to be tested.
Toggle the Appcompat flag in adb:
adb shell am compat enable RESTRICT_LOCAL_NETWORK <package_name>Reboot The device
Now your app's access to the local network is restricted and any attempt to access the local network will lead to socket errors. If you are using APIs that perform local network operations outside of your app process (ex: NsdManager), they won't be impacted during the opt-in phase.
To restore access, you must grant your app permission to NEARBY_WIFI_DEVICES.
- Ensure the app declares the
NEARBY_WIFI_DEVICESpermission in its manifest. - Go to Settings > Apps > [Application Name] > Permissions > Nearby devices > Allow.
Now your app's access to the local network should be restored and all your scenarios should work as they did prior to opting the app in.
Once enforcement for local network protection begins, here is how the app network traffic will be impacted.
| Permission | Outbound LAN Request | Outbound/Inbound Internet Request | Inbound LAN Request |
|---|---|---|---|
| Granted | Works | Works | Works |
| Not Granted | Fails | Works | Fails |
Use the following command to toggle-off the App-Compat flag
adb shell am compat disable RESTRICT_LOCAL_NETWORK <package_name>
Errors
Errors arising from these restrictions will be returned to the calling socket whenever it invokes send or a send variant to a local network address.
Example errors:
sendto failed: EPERM (Operation not permitted)

sendto failed: ECONNABORTED (Operation not permitted)
Local Network Definition
A local network in this project refers to an IP network that utilizes a broadcast-capable network interface, such as Wi-Fi or Ethernet, but excludes cellular (WWAN) or VPN connections.
The following are considered local networks:
IPv4:
- 169.254.0.0/16 // Link Local
- 100.64.0.0/10 // CGNAT
- 10.0.0.0/8 // RFC1918
- 172.16.0.0/12 // RFC1918
- 192.168.0.0/16 // RFC1918
IPv6:
- Link-local
- Directly-connected routes
- Stub networks like Thread
- Multiple-subnets (TBD)
Additionally, both multicast addresses (224.0.0.0/4, ff00::/8) and the IPv4 broadcast address (255.255.255.255) are classified as local network addresses.
Uygulamaya ait fotoğraflar
当面向 SDK 36 或更高版本的应用在搭载 Android 16 或更高版本的设备上提示用户授予照片和视频权限时,如果用户选择限制对所选媒体的访问权限,则会在照片选择器中看到该应用拥有的所有照片。用户可以取消选择任何这些预选项,这会撤消该应用对这些照片和视频的访问权限。